Microsoft
Microsoft MD-102
Endpoint Administrator
Practice questions with answers and explanations.
- 396
- Questions
- today
- Last updated
- 25
- Free questions
Question 1 of 396
Topic 1: Microsoft 365 Endpoint AdministratorTopic 1: Microsoft 365 Endpoint Administrator
HOTSPOT
Case study
Overview
ADatum Corporation is a consulting company that has a main office in Montreal and branch offices in Seattle and New York.
ADatum has a Microsoft 365 E5 subscription.
Environment
Network Environment
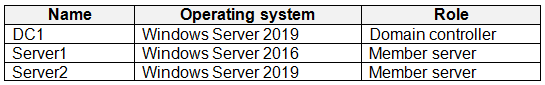
The network contains an on-premises Active Directory domain named adatum.com. The domain contains the servers shown in the following table.
ADatum has a hybrid Azure AD tenant named adatum.com.
Users and Groups
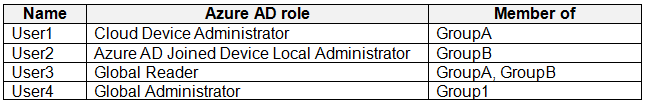
The adatum.com tenant contains the users shown in the following table.
All users are assigned a Microsoft Office 365 license and an Enterprise Mobility + Security E3 license.
Enterprise State Roaming is enabled for Group1 and GroupA.
Group1 and Group2 have a Membership type of Assigned.
Devices
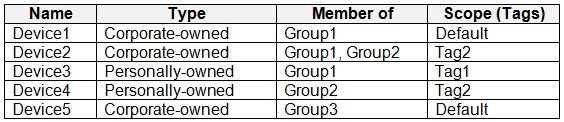
ADatum has the Windows 10 devices shown in the following table.
The Windows 10 devices are joined to Azure AD and enrolled in Microsoft Intune.
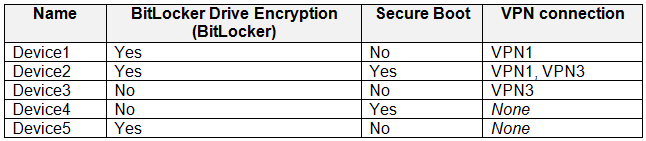
The Windows 10 devices are configured as shown in the following table.
All the Azure AD joined devices have an executable file named C:\AppA.exe and a folder named D:\Folder1.
Microsoft Intune Configuration
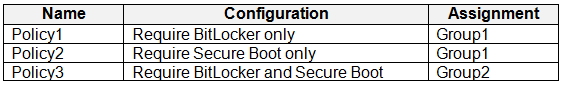
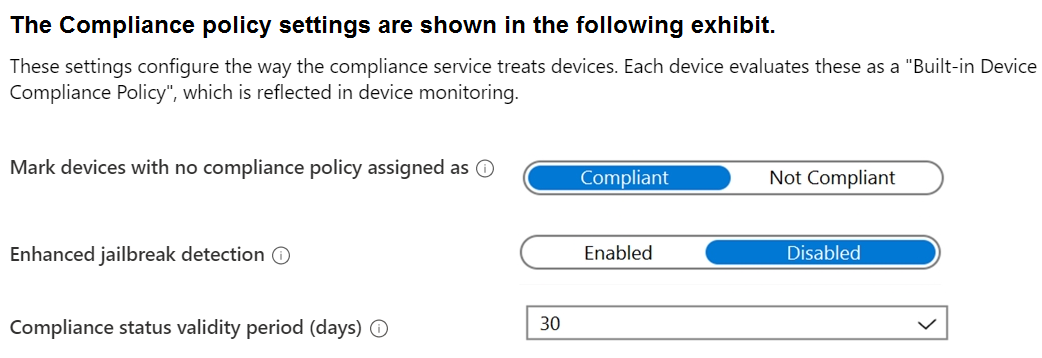
Microsoft Intune has the compliance policies shown in the following table.
The Automatic Enrollment settings have the following configurations:
MDM user scope: GroupA
MAM user scope: GroupB
You have an Endpoint protection configuration profile that has the following Controlled folder access settings:
Name: Protection1
Folder protection: Enable
List of apps that have access to protected folders: C:\*\AppA.exe
List of additional folders that need to be protected: D:\Folder1
Assignments:
Included groups: Group2, GroupB
Windows Autopilot Configuration
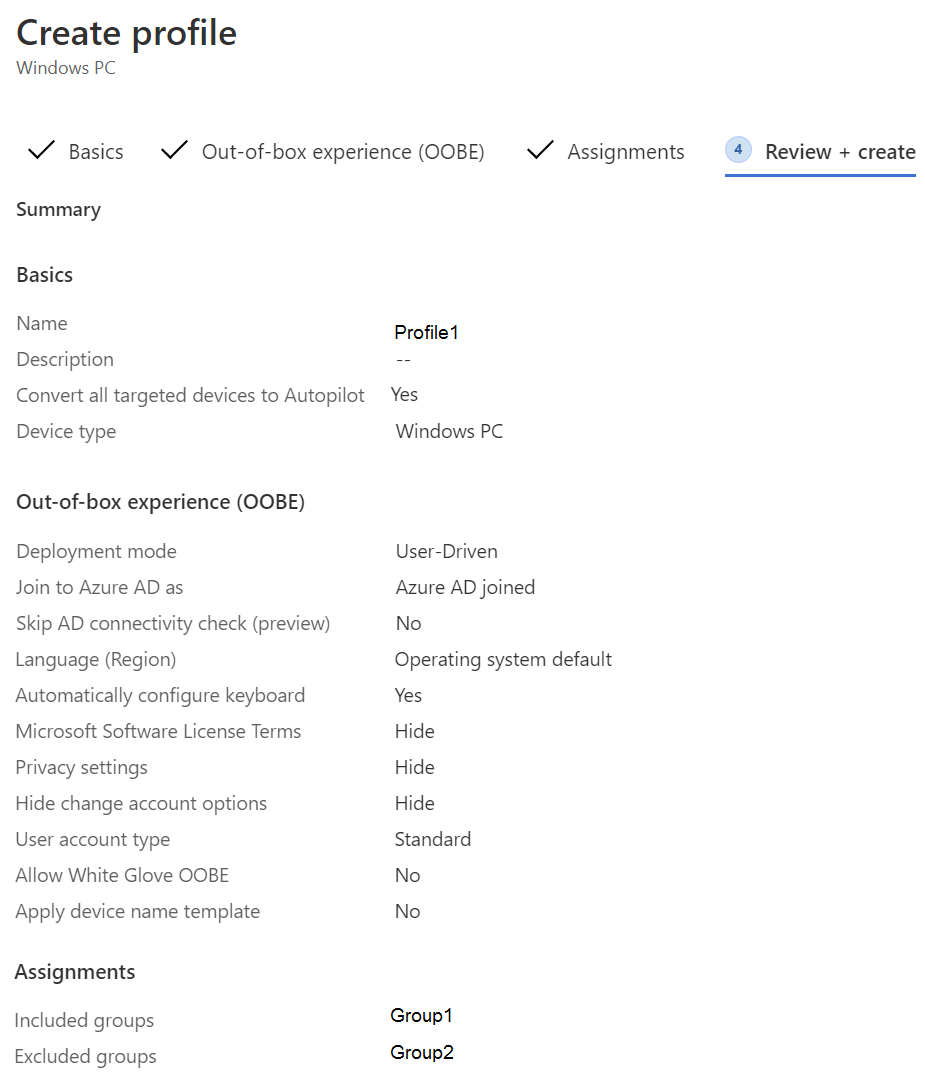
ADatum has a Windows Autopilot deployment profile configured as shown in the following exhibit.
Currently, there are no devices deployed by using Windows Autopilot.
The Intune connector for Active Directory is installed on Server1.
Requirements
Planned Changes
ADatum plans to implement the following changes:
Purchase a new Windows 10 device named Device6 and enroll the device in Intune
New computers will be deployed by using Windows Autopilot and will be hybrid Azure AD joined.
Deployed a network boundary configuration profile that will have the following settings:
Name: Boundary1
Network boundary: 192.168.1.0/24
Scope tags: Tag1
Assignments:
Included groups: Group1, Group2
Deploy two VPN configuration profiles named Connection1 and Connection2 that will have the following settings:
Name: Connection1
Connection name: VPN1
Connection type: L2TP
Assignments:
Included groups: Group1, Group2, GroupA
Excluded groups: --
Name: Connection2
Connection name: VPN2
Connection type: IKEv2
Assignments:
Included groups: GroupA
Excluded groups: GroupB
Technical Requirements
ADatum must meet the following technical requirements:
Users in GroupA must be able to deploy new computers.
Administrative effort must be minimized.
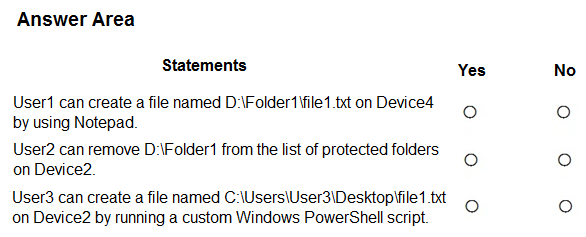
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Question 2 of 396
Topic 1: Microsoft 365 Endpoint AdministratorTopic 1: Microsoft 365 Endpoint Administrator
Case study
Overview
ADatum Corporation is a consulting company that has a main office in Montreal and branch offices in Seattle and New York.
ADatum has a Microsoft 365 E5 subscription.
Environment
Network Environment
The network contains an on-premises Active Directory domain named adatum.com. The domain contains the servers shown in the following table.
ADatum has a hybrid Azure AD tenant named adatum.com.
Users and Groups
The adatum.com tenant contains the users shown in the following table.
All users are assigned a Microsoft Office 365 license and an Enterprise Mobility + Security E3 license.
Enterprise State Roaming is enabled for Group1 and GroupA.
Group1 and Group2 have a Membership type of Assigned.
Devices
ADatum has the Windows 10 devices shown in the following table.
The Windows 10 devices are joined to Azure AD and enrolled in Microsoft Intune.
The Windows 10 devices are configured as shown in the following table.
All the Azure AD joined devices have an executable file named C:\AppA.exe and a folder named D:\Folder1.
Microsoft Intune Configuration
Microsoft Intune has the compliance policies shown in the following table.
The Automatic Enrollment settings have the following configurations:
MDM user scope: GroupA
MAM user scope: GroupB
You have an Endpoint protection configuration profile that has the following Controlled folder access settings:
Name: Protection1
Folder protection: Enable
List of apps that have access to protected folders: C:\*\AppA.exe
List of additional folders that need to be protected: D:\Folder1
Assignments:
Included groups: Group2, GroupB
Windows Autopilot Configuration
ADatum has a Windows Autopilot deployment profile configured as shown in the following exhibit.
Currently, there are no devices deployed by using Windows Autopilot.
The Intune connector for Active Directory is installed on Server1.
Requirements
Planned Changes
ADatum plans to implement the following changes:
Purchase a new Windows 10 device named Device6 and enroll the device in Intune
New computers will be deployed by using Windows Autopilot and will be hybrid Azure AD joined.
Deployed a network boundary configuration profile that will have the following settings:
Name: Boundary1
Network boundary: 192.168.1.0/24
Scope tags: Tag1
Assignments:
Included groups: Group1, Group2
Deploy two VPN configuration profiles named Connection1 and Connection2 that will have the following settings:
Name: Connection1
Connection name: VPN1
Connection type: L2TP
Assignments:
Included groups: Group1, Group2, GroupA
Excluded groups: --
Name: Connection2
Connection name: VPN2
Connection type: IKEv2
Assignments:
Included groups: GroupA
Excluded groups: GroupB
Technical Requirements
ADatum must meet the following technical requirements:
Users in GroupA must be able to deploy new computers.
Administrative effort must be minimized.
Which devices are registered by using the Windows Autopilot deployment service?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 3 of 396
Topic 1: Microsoft 365 Endpoint AdministratorTopic 1: Microsoft 365 Endpoint Administrator
HOTSPOT
Case study
Overview
ADatum Corporation is a consulting company that has a main office in Montreal and branch offices in Seattle and New York.
ADatum has a Microsoft 365 E5 subscription.
Environment
Network Environment
The network contains an on-premises Active Directory domain named adatum.com. The domain contains the servers shown in the following table.
ADatum has a hybrid Azure AD tenant named adatum.com.
Users and Groups
The adatum.com tenant contains the users shown in the following table.
All users are assigned a Microsoft Office 365 license and an Enterprise Mobility + Security E3 license.
Enterprise State Roaming is enabled for Group1 and GroupA.
Group1 and Group2 have a Membership type of Assigned.
Devices
ADatum has the Windows 10 devices shown in the following table.
The Windows 10 devices are joined to Azure AD and enrolled in Microsoft Intune.
The Windows 10 devices are configured as shown in the following table.
All the Azure AD joined devices have an executable file named C:\AppA.exe and a folder named D:\Folder1.
Microsoft Intune Configuration
Microsoft Intune has the compliance policies shown in the following table.
The Automatic Enrollment settings have the following configurations:
MDM user scope: GroupA
MAM user scope: GroupB
You have an Endpoint protection configuration profile that has the following Controlled folder access settings:
Name: Protection1
Folder protection: Enable
List of apps that have access to protected folders: C:\*\AppA.exe
List of additional folders that need to be protected: D:\Folder1
Assignments:
Included groups: Group2, GroupB
Windows Autopilot Configuration
ADatum has a Windows Autopilot deployment profile configured as shown in the following exhibit.
Currently, there are no devices deployed by using Windows Autopilot.
The Intune connector for Active Directory is installed on Server1.
Requirements
Planned Changes
ADatum plans to implement the following changes:
Purchase a new Windows 10 device named Device6 and enroll the device in Intune
New computers will be deployed by using Windows Autopilot and will be hybrid Azure AD joined.
Deployed a network boundary configuration profile that will have the following settings:
Name: Boundary1
Network boundary: 192.168.1.0/24
Scope tags: Tag1
Assignments:
Included groups: Group1, Group2
Deploy two VPN configuration profiles named Connection1 and Connection2 that will have the following settings:
Name: Connection1
Connection name: VPN1
Connection type: L2TP
Assignments:
Included groups: Group1, Group2, GroupA
Excluded groups: --
Name: Connection2
Connection name: VPN2
Connection type: IKEv2
Assignments:
Included groups: GroupA
Excluded groups: GroupB
Technical Requirements
ADatum must meet the following technical requirements:
Users in GroupA must be able to deploy new computers.
Administrative effort must be minimized.
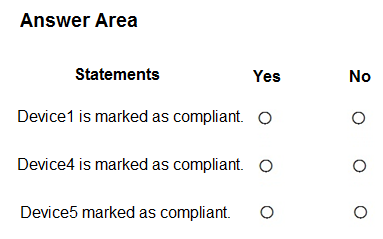
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Question 4 of 396
Topic 1: Microsoft 365 Endpoint AdministratorTopic 1: Microsoft 365 Endpoint Administrator
Case study
Overview
ADatum Corporation is a consulting company that has a main office in Montreal and branch offices in Seattle and New York.
ADatum has a Microsoft 365 E5 subscription.
Environment
Network Environment
The network contains an on-premises Active Directory domain named adatum.com. The domain contains the servers shown in the following table.
ADatum has a hybrid Azure AD tenant named adatum.com.
Users and Groups
The adatum.com tenant contains the users shown in the following table.
All users are assigned a Microsoft Office 365 license and an Enterprise Mobility + Security E3 license.
Enterprise State Roaming is enabled for Group1 and GroupA.
Group1 and Group2 have a Membership type of Assigned.
Devices
ADatum has the Windows 10 devices shown in the following table.
The Windows 10 devices are joined to Azure AD and enrolled in Microsoft Intune.
The Windows 10 devices are configured as shown in the following table.
All the Azure AD joined devices have an executable file named C:\AppA.exe and a folder named D:\Folder1.
Microsoft Intune Configuration
Microsoft Intune has the compliance policies shown in the following table.
The Automatic Enrollment settings have the following configurations:
MDM user scope: GroupA
MAM user scope: GroupB
You have an Endpoint protection configuration profile that has the following Controlled folder access settings:
Name: Protection1
Folder protection: Enable
List of apps that have access to protected folders: C:\*\AppA.exe
List of additional folders that need to be protected: D:\Folder1
Assignments:
Included groups: Group2, GroupB
Windows Autopilot Configuration
ADatum has a Windows Autopilot deployment profile configured as shown in the following exhibit.
Currently, there are no devices deployed by using Windows Autopilot.
The Intune connector for Active Directory is installed on Server1.
Requirements
Planned Changes
ADatum plans to implement the following changes:
Purchase a new Windows 10 device named Device6 and enroll the device in Intune
New computers will be deployed by using Windows Autopilot and will be hybrid Azure AD joined.
Deployed a network boundary configuration profile that will have the following settings:
Name: Boundary1
Network boundary: 192.168.1.0/24
Scope tags: Tag1
Assignments:
Included groups: Group1, Group2
Deploy two VPN configuration profiles named Connection1 and Connection2 that will have the following settings:
Name: Connection1
Connection name: VPN1
Connection type: L2TP
Assignments:
Included groups: Group1, Group2, GroupA
Excluded groups: --
Name: Connection2
Connection name: VPN2
Connection type: IKEv2
Assignments:
Included groups: GroupA
Excluded groups: GroupB
Technical Requirements
ADatum must meet the following technical requirements:
Users in GroupA must be able to deploy new computers.
Administrative effort must be minimized.
You implement Boundary1 based on the planned changes.
Which devices have a network boundary of 192.168.1.0/24 applied?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 5 of 396
Topic 1: Microsoft 365 Endpoint AdministratorTopic 1: Microsoft 365 Endpoint Administrator
HOTSPOT
You have a Microsoft 365 subscription.
You use Microsoft Intune Suite to manage devices.
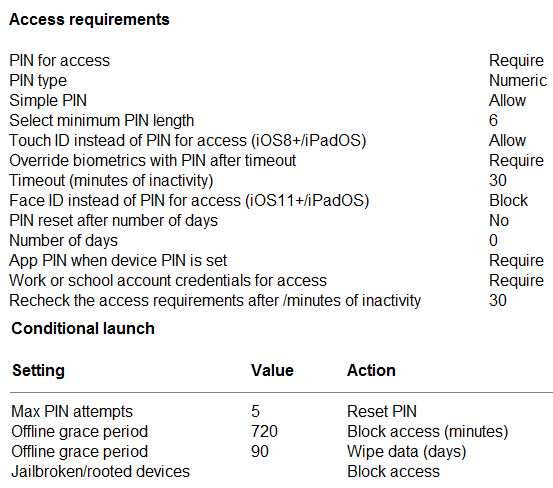
You have the iOS app protection policy shown in the following exhibit.
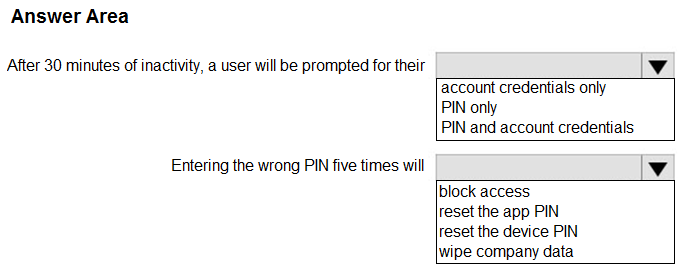
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.