Microsoft
Microsoft SC-200
Microsoft Security Operations Analyst
Practice questions with answers and explanations.
- 395
- Questions
- today
- Last updated
- 25
- Free questions
Question 11 of 395
Topic 1: Mitigate threats by using Microsoft Defender XDRTopic 1: Mitigate threats by using Microsoft Defender XDR
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might
meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring Microsoft Defender for Identity integration with Active Directory.
From the Microsoft Defender for identity portal, you need to configure several accounts for attackers to exploit.
Solution: From Azure AD Identity Protection, you configure the sign-in risk policy.
Does this meet the goal?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 12 of 395
Topic 1: Mitigate threats by using Microsoft Defender XDRTopic 1: Mitigate threats by using Microsoft Defender XDR
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might
meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You are configuring Microsoft Defender for Identity integration with Active Directory.
From the Microsoft Defender for identity portal, you need to configure several accounts for attackers to exploit.
Solution: You add the accounts to an Active Directory group and add the group as a Sensitive group.
Does this meet the goal?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 13 of 395
Topic 1: Mitigate threats by using Microsoft Defender XDRTopic 1: Mitigate threats by using Microsoft Defender XDR
You implement Safe Attachments policies in Microsoft Defender for Office 365.
Users report that email messages containing attachments take longer than expected to be received.
You need to reduce the amount of time it takes to deliver messages that contain attachments without compromising security. The attachments must be scanned
for malware, and any messages that contain malware must be blocked.
What should you configure in the Safe Attachments policies?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 14 of 395
Topic 1: Mitigate threats by using Microsoft Defender XDRTopic 1: Mitigate threats by using Microsoft Defender XDR
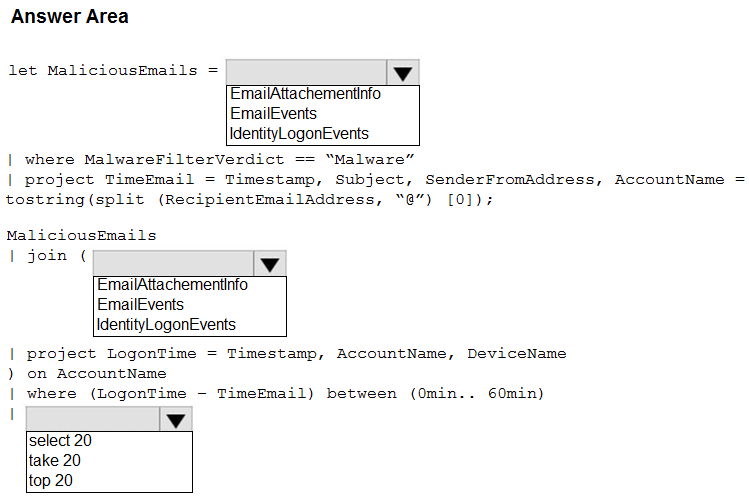
HOTSPOT
You are informed of an increase in malicious email being received by users.
You need to create an advanced hunting query in Microsoft 365 Defender to identify whether the accounts of the email recipients were compromised. The query
must return the most recent 20 sign-ins performed by the recipients within an hour of receiving the known malicious email.
How should you complete the query? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Question 15 of 395
Topic 1: Mitigate threats by using Microsoft Defender XDRTopic 1: Mitigate threats by using Microsoft Defender XDR
You receive a security bulletin about a potential attack that uses an image file.
You need to create an indicator of compromise (IoC) in Microsoft Defender for Endpoint to prevent the attack.
Which indicator type should you use?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.