CompTIA
CompTIA CAS-005
CompTIA SecurityX
Practice questions with verified answers, detailed explanations, and community discussions.
- 399
- Questions
- today
- Last updated
- Guest
- Your plan
25 free questions
Question 1 of 399
Topic 1: CompTIA SecurityX CAS-005Topic 1: CompTIA SecurityX CAS-005
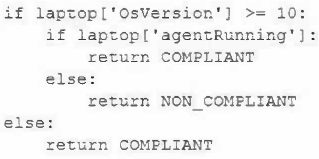
A security engineer is reviewing event logs because an employee successfully connected a personal Windows laptop to the corporate network, which is against company policy. Company policy allows all Windows 10 and 11 laptops to connect to the system as long as the MDM agent installed by IT is running. Only compliant devices can connect, and the logic in the system to evaluate compliant laptops is as follows:
Which of the following most likely occurred when the employee connected a personally owned Windows laptop and was allowed on the network?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 2 of 399
Topic 1: CompTIA SecurityX CAS-005Topic 1: CompTIA SecurityX CAS-005
An organization is working to secure its development process to ensure developers cannot deploy artifacts directly into the production environment. Which of the following security practice recommendations would be the best to accomplish this objective?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 3 of 399
Topic 1: CompTIA SecurityX CAS-005Topic 1: CompTIA SecurityX CAS-005
A security architect discovers the following while reviewing code for a company's website:
selection = "SELECT Item FROM Catalog WHERE ItemID = " & Request("ItemID")
Which of the following should the security architect recommend?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 4 of 399
Topic 1: CompTIA SecurityX CAS-005Topic 1: CompTIA SecurityX CAS-005
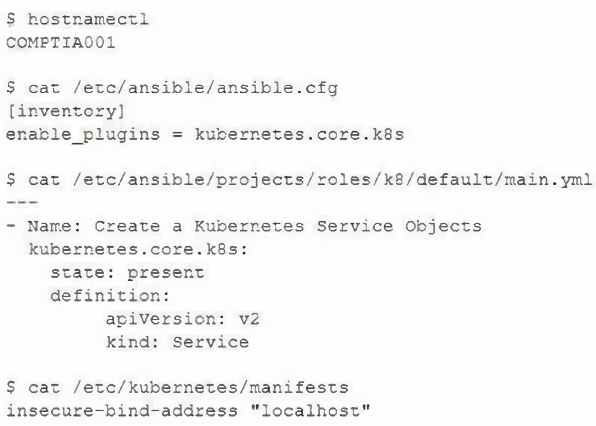
A security architect needs to enable a container orchestrator for DevSecOps and SOAR initiatives. The engineer has discovered that several Ansible YAML files used for the automation of configuration management have the following content:
Which of the following should the engineer do to correct the security issues presented within this content?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 5 of 399
Topic 1: CompTIA SecurityX CAS-005Topic 1: CompTIA SecurityX CAS-005
A CRM company leverages a CSP PaaS service to host and publish Its SaaS product. Recently, a large customer requested that all infrastructure components must meet strict regulatory requirements, including configuration management, patch management, and life-cycle management. Which of the following organizations is responsible for ensuring those regulatory requirements are met?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.