CompTIA
CompTIA CAS-005
CompTIA SecurityX
Practice questions with verified answers, detailed explanations, and community discussions.
- 399
- Questions
- today
- Last updated
- Guest
- Your plan
25 free questions
Question 16 of 399
Topic 1: CompTIA SecurityX CAS-005Topic 1: CompTIA SecurityX CAS-005
Which of the following best explain why organizations prefer to utilize code that is digitally signed? (Choose two.)
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 17 of 399
Topic 1: CompTIA SecurityX CAS-005Topic 1: CompTIA SecurityX CAS-005
A security engineer receives reports through the organization's bug bounty program about remote code execution in a specific component in a custom application. Management wants to properly secure the component and proactively avoid similar issues. Which of the following is the best approach to uncover additional vulnerable paths in the application?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 18 of 399
Topic 1: CompTIA SecurityX CAS-005Topic 1: CompTIA SecurityX CAS-005
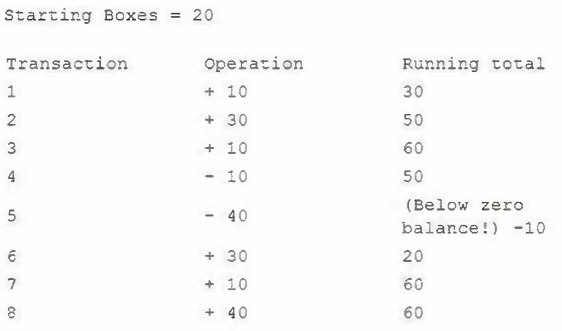
A security technician is investigating a system that tracks inventory via a batch update each night. The technician is concerned that the system poses a risk to the business, as errors are occasionally generated and reported inventory appears incorrect. The following output log is provided:
The technician reviews the output of the batch job and discovers that the inventory was never less than zero, and the final inventory was 100 rather than 60. Which of the following should the technician do to resolve this issue?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 19 of 399
Topic 1: CompTIA SecurityX CAS-005Topic 1: CompTIA SecurityX CAS-005
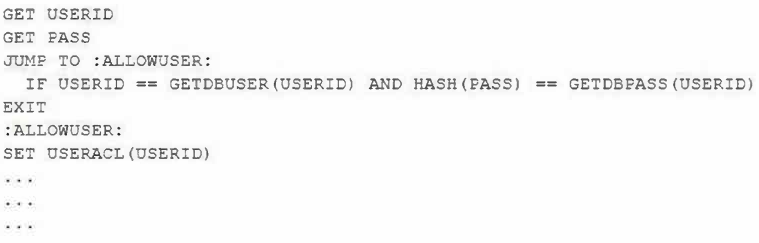
A programmer is reviewing the following proprietary piece of code that was identified as a vulnerability due to users being authenticated when they provide incorrect credentials:
Which of the following should the programmer implement to remediate the code vulnerability?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 20 of 399
Topic 1: CompTIA SecurityX CAS-005Topic 1: CompTIA SecurityX CAS-005
A senior cybersecurity engineer is solving a digital certificate issue in which the CA denied certificate issuance due to failed subject identity validation. At which of the following steps within the PKI enrollment process would the denial have occurred?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.