CompTIA
CompTIA CS0-003
CompTIA Cybersecurity Analyst (CySA+)
Practice questions with verified answers, detailed explanations, and community discussions.
- 531
- Questions
- today
- Last updated
- Guest
- Your plan
25 free questions
Question 1 of 531
Topic 1: CompTIA CySA+ CS0-003Topic 1: CompTIA CySA+ CS0-003
A recent zero-day vulnerability is being actively exploited, requires no user interaction or privilege escalation, and has a significant impact to confidentiality and integrity but not to availability. Which of the following CVE metrics would be most accurate for this zero-day threat?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 2 of 531
Topic 1: CompTIA CySA+ CS0-003Topic 1: CompTIA CySA+ CS0-003
Which of the following tools would work best to prevent the exposure of PII outside of an organization?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 3 of 531
Topic 1: CompTIA CySA+ CS0-003Topic 1: CompTIA CySA+ CS0-003
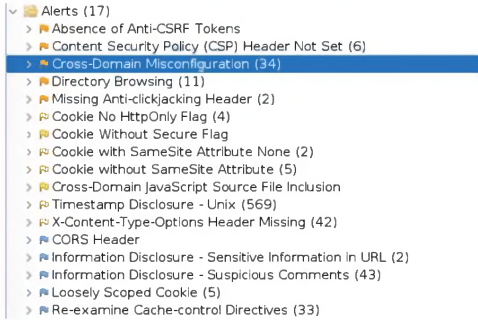
An organization conducted a web application vulnerability assessment against the corporate website, and the following output was observed:
Which of the following tuning recommendations should the security analyst share?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 4 of 531
Topic 1: CompTIA CySA+ CS0-003Topic 1: CompTIA CySA+ CS0-003
Which of the following items should be included in a vulnerability scan report? (Choose two.)
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 5 of 531
Topic 1: CompTIA CySA+ CS0-003Topic 1: CompTIA CySA+ CS0-003
The Chief Executive Officer of an organization recently heard that exploitation of new attacks in the industry was happening approximately 45 days after a patch was released. Which of the following would best protect this organization?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.