CompTIA
CompTIA CS0-003
CompTIA Cybersecurity Analyst (CySA+)
Practice questions with verified answers, detailed explanations, and community discussions.
- 531
- Questions
- today
- Last updated
- Guest
- Your plan
25 free questions
Question 16 of 531
Topic 1: CompTIA CySA+ CS0-003Topic 1: CompTIA CySA+ CS0-003
An analyst is reviewing a vulnerability report and must make recommendations to the executive team. The analyst finds that most systems can be upgraded with a reboot resulting in a single downtime window. However, two of the critical systems cannot be upgraded due to a vendor appliance that the company does not have access to. Which of the following inhibitors to remediation do these systems and associated vulnerabilities best represent?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 17 of 531
Topic 1: CompTIA CySA+ CS0-003Topic 1: CompTIA CySA+ CS0-003
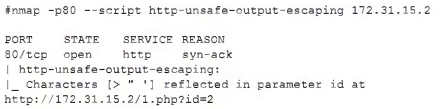
The security team reviews a web server for XSS and runs the following Nmap scan:
Which of the following most accurately describes the result of the scan?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 18 of 531
Topic 1: CompTIA CySA+ CS0-003Topic 1: CompTIA CySA+ CS0-003
Which of the following is the best action to take after the conclusion of a security incident to improve incident response in the future?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 19 of 531
Topic 1: CompTIA CySA+ CS0-003Topic 1: CompTIA CySA+ CS0-003
A security analyst received a malicious binary file to analyze. Which of the following is the best technique to perform the analysis?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 20 of 531
Topic 1: CompTIA CySA+ CS0-003Topic 1: CompTIA CySA+ CS0-003
An incident response team found IoCs in a critical server. The team needs to isolate and collect technical evidence for further investigation. Which of the following pieces of data should be collected first in order to preserve sensitive information before isolating the server?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.