CompTIA
CompTIA CS0-003
CompTIA Cybersecurity Analyst (CySA+)
Practice questions with verified answers, detailed explanations, and community discussions.
- 531
- Questions
- today
- Last updated
- Guest
- Your plan
25 free questions
Question 6 of 531
Topic 1: CompTIA CySA+ CS0-003Topic 1: CompTIA CySA+ CS0-003
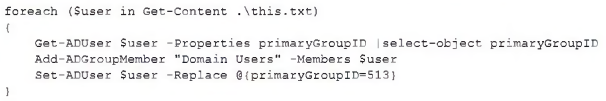
A security analyst recently joined the team and is trying to determine which scripting language is being used in a production script to determine if it is malicious. Given the following script:
Which of the following scripting languages was used in the script?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 7 of 531
Topic 1: CompTIA CySA+ CS0-003Topic 1: CompTIA CySA+ CS0-003
A company's user accounts have been compromised. Users are also reporting that the company's internal portal is sometimes only accessible through HTTP, other times; it is accessible through HTTPS. Which of the following most likely describes the observed activity?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 8 of 531
Topic 1: CompTIA CySA+ CS0-003Topic 1: CompTIA CySA+ CS0-003
A security analyst is tasked with prioritizing vulnerabilities for remediation. The relevant company security policies are shown below:
Security Policy 1006: Vulnerability Management
1. The Company shall use the CVSSv3.1 Base Score Metrics (Exploitability and Impact) to prioritize the remediation of security vulnerabilities.
2. In situations where a choice must be made between confidentiality and availability, the Company shall prioritize confidentiality of data over availability of systems and data.
3. The Company shall prioritize patching of publicly available systems and services over patching of internally available system.
According to the security policy, which of the following vulnerabilities should be the highest priority to patch?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 9 of 531
Topic 1: CompTIA CySA+ CS0-003Topic 1: CompTIA CySA+ CS0-003
Which of the following will most likely ensure that mission-critical services are available in the event of an incident?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.
Question 10 of 531
Topic 1: CompTIA CySA+ CS0-003Topic 1: CompTIA CySA+ CS0-003
The Chief Information Security Officer wants to eliminate and reduce shadow IT in the enterprise. Several high-risk cloud applications are used that increase the risk to the organization. Which of the following solutions will assist in reducing the risk?
Choose your answer
Pick an answer to check it, or press Show answer to see the correct one.